Quiz Entry - updated: 2026.10.22
How is the Swiss E-ID trust infrastructure structured?
Three zones: an issuing ecosystem (e.g. fedpol for the E-ID, the road traffic offices for driving credentials), the state trust infrastructure run by the Federal Office of Justice with the FOITT (wallet app, base and trust registers, portal), and a verifying ecosystem of verifiers.
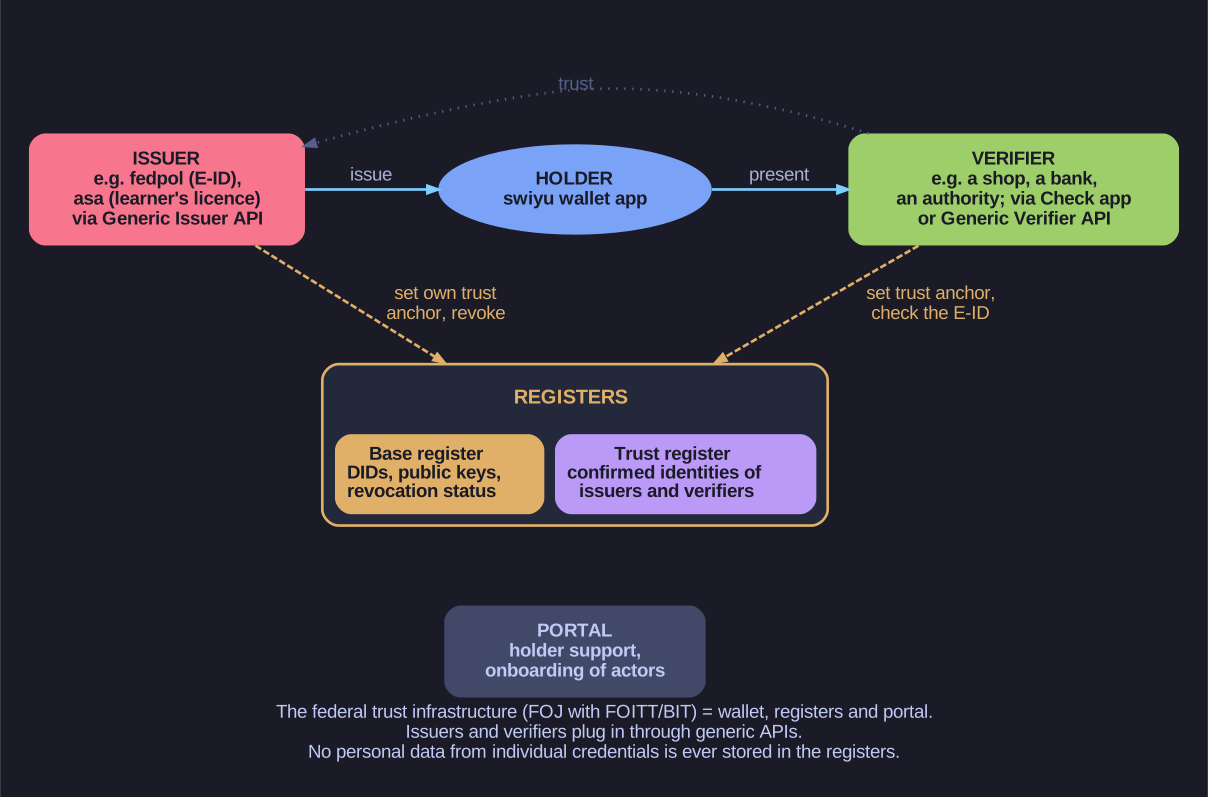
* The state runs the wallet, registers and portal; issuers and verifiers connect through generic APIs. *
- Issuing ecosystem: issuers such as fedpol (the E-ID) or the road traffic authorities (learner's or driving licence) issue credentials into the holder's wallet, using a generic issuer API.
- Trust infrastructure (FOJ with the FOITT, the federal IT office):
- The wallet app (swiyu), where the holder keeps credentials.
- The register, in two parts: the base register (identifiers, public keys, revocation status) and the trust register (confirmed identities of issuers and verifiers). Issuers set their own trust anchors there and revoke credentials; verifiers read trust anchors and check the E-ID.
- A portal for holder support and onboarding of new issuers and verifiers.
- Verifying ecosystem: verifiers check presented credentials, using a check app or a generic verifier API.
Holders present directly to verifiers. Issuers and verifiers are connected only through trust, via the registers, never by direct data exchange about the holder.
Go deeper:
 e-ID: Technologie (eid.admin.ch) — the official description of the ecosystem and registers (in German).
- swiyu technical documentation — the developer docs for issuers, verifiers and the registers.