Finance administration F modernised its decades-old IT in three steps. In step 1, a mainframe-based finance system was migrated to a Unix cluster with dedicated client software on office PCs. Which security model applied before and after this step?
Before: the mainframe and its input terminals sat in the data-centre room, so the system was protected by security-by-isolation (system boundary = the room). After: the Unix cluster in the data centre is accessed by fclient.exe from the office building through a firewall (allow ip-range-client -> ip-range-unix-cluster, protocol fclient; deny *) — a simple perimeter security.
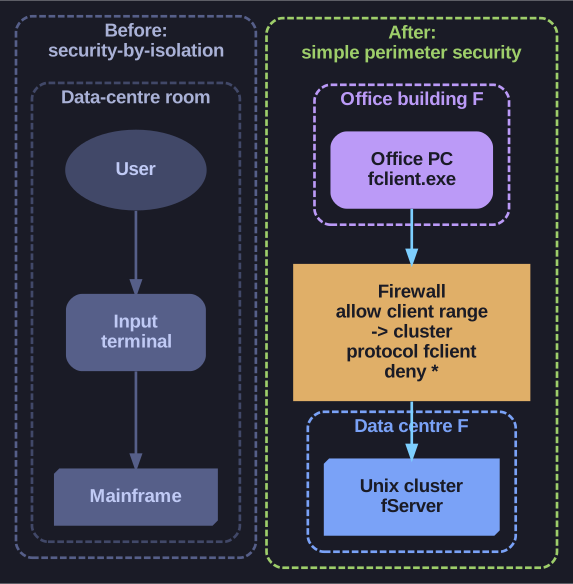
* From one room to two buildings: the isolation of the mainframe room is replaced by a firewall between data centre and offices. *
With the mainframe, nobody outside the room could reach the system at all: the input terminals were in the same room (Rechenzentrum, data centre). Moving to client software on ordinary office PCs extends the system across the data-centre perimeter into the office building (Bürogebäude). The firewall now carries the protection: only the client address range may reach the cluster, only with the system's own protocol, and everything else is denied.
The step shows how a security architecture changes when the access path changes, even though the business system stays the same.
Go deeper:
 Mainframe computer — Wikipedia — the centralised machines with local terminals the finance system started on.
- Rich client — Wikipedia — client software installed on each PC, like
fclient.exe.