Question
Why did plain perimeter security become "leaky" once companies started offering services on the internet, and what was the motivation for the DMZ?
Answer
Internet-facing servers (web server, email exchanger, DNS, web application) sat inside the same internal LAN as everything else, so the few systems that talk to the outside endangered the many systems that only interact internally. Once one of them was compromised, an attacker could move laterally to the inventory system, CRM, accounting servers and database unhindered.
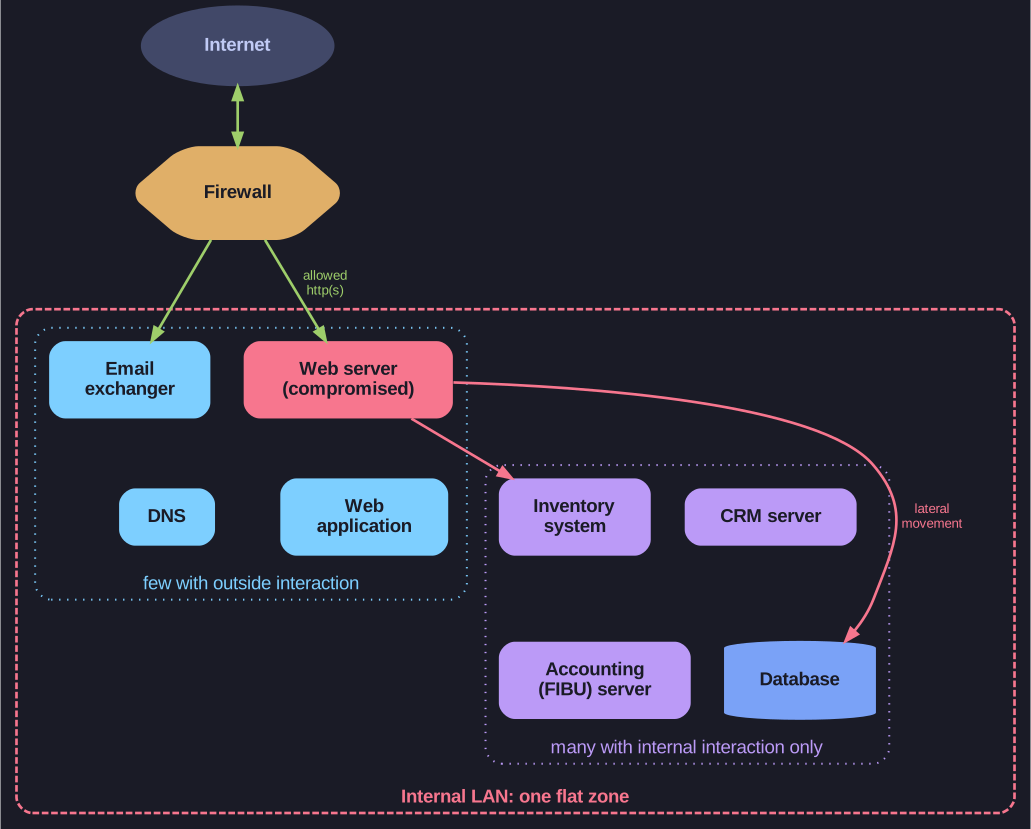
* A few servers face the internet, but they share one flat LAN with everything that should never be reachable from outside. *
A perimeter only knows "inside" and "outside". As more business cases required an internet presence or active participation on the internet, more inside systems needed holes in the firewall so the outside could reach them. Each hole lands inside the trusted zone. The development reached a first peak during the dot-com boom around 2000, when almost every company put a website, a mail exchanger and public DNS online.
The problem is the mismatch of exposure: a web server is attacked all day long, while the accounting (FIBU, Finanzbuchhaltung) server never needs to talk to the internet at all. Putting both in one flat zone means the security of the accounting server is only as good as that of the web server. This is the flat perimeter anti-pattern applied to internet services, and the idea of the DMZ grew out of exactly this motivation.
Go deeper:
 Lateral movement (cybersecurity) — Wikipedia — how an attacker spreads from one foothold through a flat network.
- Dot-com bubble — Wikipedia — the late-1990s rush online that put internet-facing servers into every company.
Note saved — thanks!
Question
What is a DMZ in IT, where does the term come from, and which systems belong in it?
Answer
A DMZ (demilitarised zone) is a network segment placed between two security zones, typically between the internal network and the internet. It holds the servers and services that must be reachable from the internet, such as web server, email exchanger, DNS and web application, and access to it is strictly regulated.
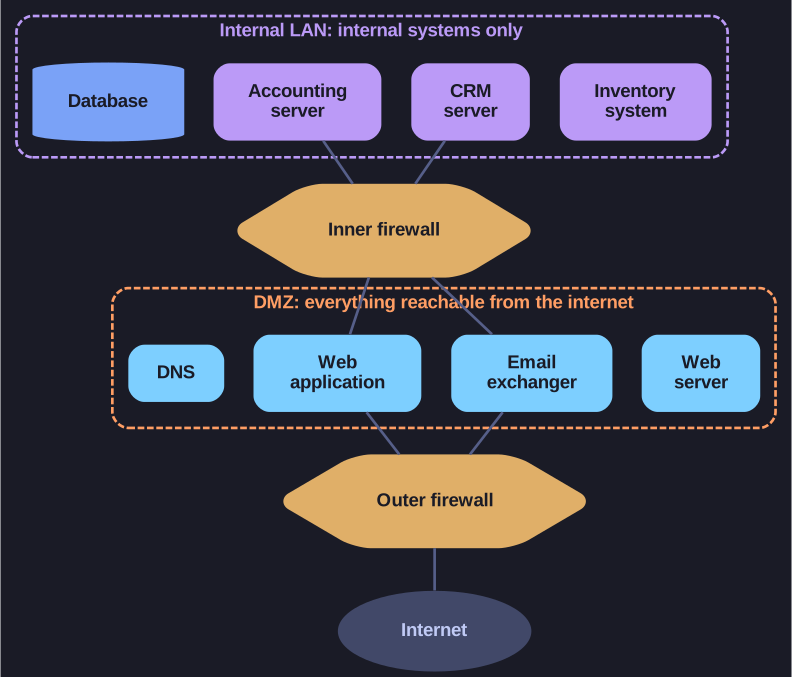
* Three zones instead of two: the internet-facing servers move out of the LAN into their own segment between two firewalls. *
The term is borrowed from geopolitics: a demilitarised zone is an area, typically a border strip between two rival states, where no military may be stationed or moved. In IT the meaning is adapted: the DMZ is a buffer that belongs neither to the trusted inside nor to the hostile outside.
Compared with the flat LAN, the internet-facing servers are moved out into their own segment. The internal systems (inventory, CRM, accounting servers, the database) stay in the internal LAN, and a firewall on each side of the DMZ controls what may cross.
Go deeper:
- DMZ (computing) — Wikipedia — single-firewall versus dual-firewall DMZ designs and which services go in it.
- Demilitarized zone — Wikipedia — the military origin of the term.
Note saved — thanks!