Besides classic request filtering, which additional functions are WAFs often extended with?
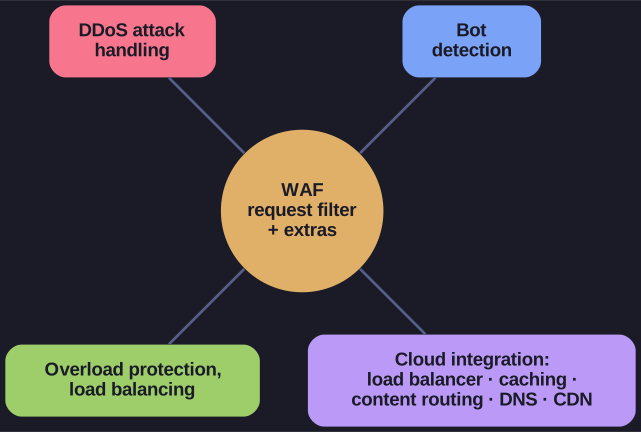
Bot detection, handling of DDoS attacks, and overload protection / load balancing. Modern combined solutions also integrate with further components of the cloud provider, such as load balancers, caching frameworks, content routing, DNS and content-delivery frameworks.
* Because all traffic passes through the WAF anyway, it is the natural place to add more functions. *
These additions follow from the WAF's position: it already terminates every request to the application, so it can count, classify and steer them. Bot detection separates automated clients (scrapers, credential-stuffing tools) from humans. DDoS handling absorbs or drops floods of requests before they reach the servers. Overload protection and load balancing spread legitimate load over several servers. In a cloud, the WAF then becomes one part of a larger delivery chain together with DNS, CDN and caching.
Go deeper:
 Introduction to Azure Web Application Firewall — Microsoft Learn — a WAF integrated into Application Gateway and Front Door, with bot protection.
- Google Cloud Armor — Preconfigured WAF rules overview — a cloud WAF's rule sets and sensitivity levels.
- DDoS mitigation — Wikipedia — how floods are detected and absorbed in front of a service.