Quiz Entry - updated: 2026.11.05
A playbook loads a vault-encrypted file. What happens if you run it without the vault password, and what are the three ways to provide it?
It fails with an error such as "Attempting to decrypt but no vault secrets found". Provide the password (1) interactively, (2) from a password file with --vault-password-file, or (3) via the environment variable ANSIBLE_VAULT_PASSWORD_FILE, which points to such a file.
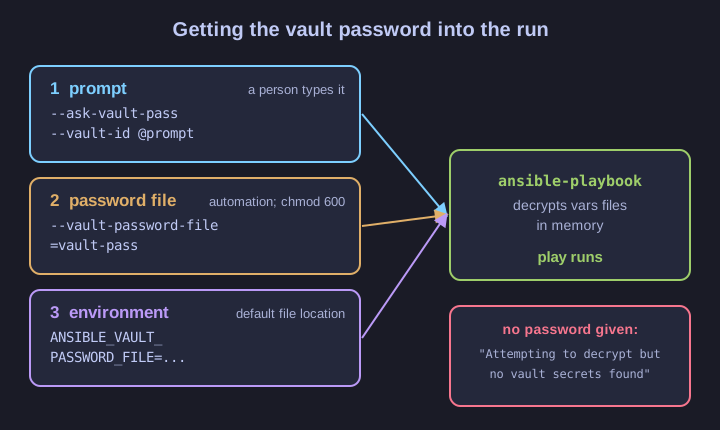
| Way | ansible-playbook |
ansible-navigator |
|---|---|---|
| Interactive prompt | --ask-vault-pass (or --vault-id @prompt) |
--vault-id @prompt plus --pae false |
| Password file | --vault-password-file=vault-pass |
same option |
| Environment variable | export ANSIBLE_VAULT_PASSWORD_FILE=~/vault-pass |
same |
Choosing one:
- Prompt for a human at a terminal: nothing secret is stored anywhere.
- Password file or the environment variable for automation (CI, scheduled runs), where no one is there to type. The file holds the password as a single line of plain text, so it must be protected with file permissions and kept out of the repository.
Even --syntax-check needs the password, because Ansible has to decrypt vars_files to load the play.
Go deeper:
 Using encrypted variables and files (official docs) — passing passwords at run time.
- Managing vault passwords (official docs) — password files, scripts and vault IDs.