Question
What are the three most important types of cryptographic attacks, ranked from weakest to strongest attacker model?
Answer
Ciphertext-only (weakest), known-plaintext, and chosen-plaintext (strongest) — each gives the attacker progressively more information.
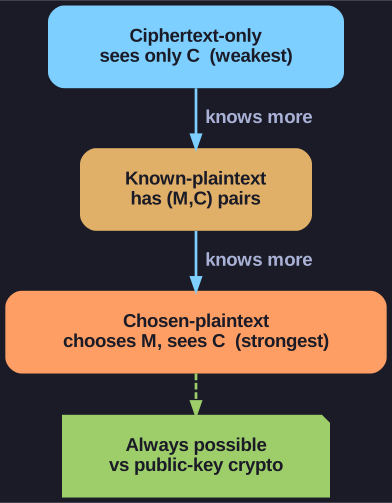
* The three attacker models in increasing power — each grants strictly more information than the last. *
I) Ciphertext-Only Attack:
- Known: Only the ciphertext (intercepted from the channel)
- Goal: Find the plaintext and/or the key
- Weakest attacker model — the minimum any eavesdropper has
II) Known-Plaintext Attack:
- Known: Pairs of plaintext and corresponding ciphertext $(M_i, C_i)$
- Goal: Find the key (and decrypt other messages)
- Example: Exploiting known headers like "Dear Sir/Madam" or "Sincerely" in encrypted emails
III) Chosen-Plaintext Attack:
- Known: The attacker can choose any plaintext and get its ciphertext (access to the encryption device)
- Goal: Find the key (knowing the plaintext is no longer the goal — the attacker already chooses it)
- Strongest attacker model for symmetric ciphers
Critical insight: A chosen-plaintext attack is always possible against public-key encryption, because anyone can encrypt any message using the public key. This is why public-key systems must be designed to resist this attack by default.
Go deeper:
 Chosen-plaintext attack (Wikipedia) — the strongest standard model, and why public-key crypto always faces it.
- Known-plaintext attack (Wikipedia) — cribs at Bletchley Park and beyond.
Note saved — thanks!
Question
Which common hash functions are considered deprecated, and which are currently recommended?
Answer
MD5 (128-bit) and SHA-1 (160-bit) are deprecated and must not be used for signatures; SHA-2 (256/512-bit) and SHA-3 are currently recommended.
| Hash Function | Output Size | Status |
|---|---|---|
| MD5 | 128 bits | Broken — collisions found in 2004, practical attacks exist |
| SHA-1 | 160 bits | Deprecated — collision found by Google in 2017 (SHAttered) |
| SHA-2 (SHA-256, SHA-512) | 256 / 512 bits | Recommended — currently standard |
| SHA-3 (Keccak) | 256 / 512 bits | Recommended — different internal structure from SHA-2 |
Why does this matter? If an attacker can find collisions in a hash function, they can forge digital signatures. For example, they could create two documents with the same hash — one innocent, one malicious — get the innocent one signed, then substitute the malicious one.
Tip: SHA-2 and SHA-3 are both secure, but they use fundamentally different internal designs (Merkle-Damgård vs. sponge construction). Having both provides defense in depth — if one design is broken, the other likely survives.
Go deeper:
- SHA-1 — the deprecation history and the SHAttered break.
 SHAttered — first SHA-1 collision — two different PDFs with the same SHA-1 hash, with downloadable proof.
- MD5 — why MD5 is catastrophically broken for signatures.

Note saved — thanks!