Question
What is the Mehrlinien-Organisation (multi-line organization)?
Answer
An organization where employees report to several superiors at once — specialization at the management level, at the cost of unity of command.
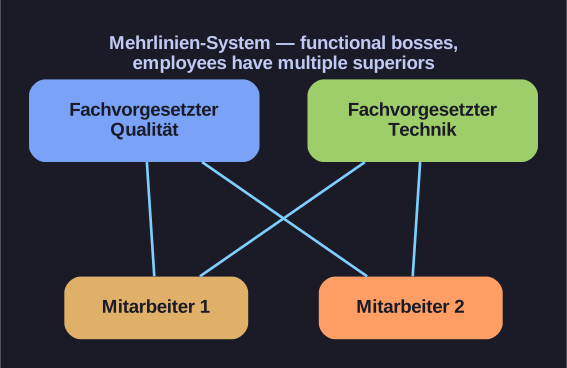
* Mehrlinien-System — Taylor's functional foremen; each employee answers to several superiors. *
In the Mehrlinien-System (going back to F.W. Taylor's "functional foremen"), an employee receives instructions from multiple specialized supervisors, each authoritative for their own subject area.
Advantages:
- Direct, short paths to the relevant specialist boss
- Managers can specialize instead of judging everything
- Decisions by those with the deepest expertise
Disadvantages:
- Violates unity of command — conflicting instructions are built in
- Competence conflicts and unclear responsibility ("which boss wins?")
- High coordination effort
Tip: The matrix organization is the modern, systematized descendant of this idea — two formalized lines (functional + project/product) instead of many informal ones. Whenever you see "two bosses," think: who resolves conflicts, and is that resolution path defined?
Go deeper:
 Linienorganisation (Wikipedia DE) — Das Mehrliniensystem nach Taylors functional foremen und der Bruch der Einheit der Auftragserteilung.
Note saved — thanks!
Question
Using "Vulnerability & Patch Management" as an example SCF domain, what does an individual SCF control entry look like?
Answer
In the Secure Controls Framework (SCF) — the free "framework of frameworks" cybersecurity/privacy control catalog — each control row has a Domain, a named Control, an SCF control number, and a description of the mechanism that must exist — e.g. VPM-06 "Vulnerability Scanning" requires mechanisms to detect vulnerabilities by routine scanning.
In the Vulnerability & Patch Management domain, example controls include:
| SCF # | Control | What it requires |
|---|---|---|
| VPM-05.2 | Automated Remediation Status | Mechanisms to determine the state of components regarding flaw remediation |
| VPM-06 | Vulnerability Scanning | Mechanisms to detect vulnerabilities/misconfigurations by routine scanning |
| VPM-06.3 | Privileged Access | Mechanisms to implement privileged access authorization for selected scans |
This single domain spans ~33 controls covering vulnerability ranking, trend analysis, internal + external assessment scans, penetration testing, and red-team exercises.
Go deeper:
- Vulnerability management — Wikipedia — Der Zyklus aus Erkennen, Priorisieren (z. B. CVSS) und Beheben von Schwachstellen, den VPM-Controls fordern.
Note saved — thanks!