Question
Why must a developer's code-signing certificate be added to "Trusted Publishers" even though the company CA already issued it?
Answer
A trusted chain only proves who signed; AllSigned additionally asks whether you want to run code from that publisher, and only certificates in the Trusted Publishers store run without that question.
Windows separates two questions:
- Is the signature valid? The certificate must chain to a trusted root, be valid and have the code-signing EKU. The company CA already guarantees that.
- Do I want code from this publisher? That is answered by the Trusted Publishers certificate store. Under AllSigned, a script from a publisher not in that store triggers a prompt ("Do you want to run software from this untrusted publisher?"), which blocks unattended use.
Deploying the certificate to the store with Group Policy makes the decision once, centrally: export the developer's code-signing certificate (Base64, without the private key) from the CA, import it under Computer Configuration, Policies, Windows Settings, Security Settings, Public Key Policies, Trusted Publishers, run gpupdate /force, and check in certlm.msc (the local computer store) that it arrived.
This is an allowlist of individuals, more specific than "anything the CA ever signed". A certificate the CA issued to someone else for code signing is still asked about.
Go deeper:
 Microsoft Learn: about_Signing — how PowerShell treats trusted and untrusted publishers under AllSigned.
Note saved — thanks!
Question
How does the octal (absolute) notation of chmod work, and what are chmod 644 and chmod 600?
Answer
Each right has a value (r = 4, w = 2, x = 1); add them per class to get one digit each for user, group and others.
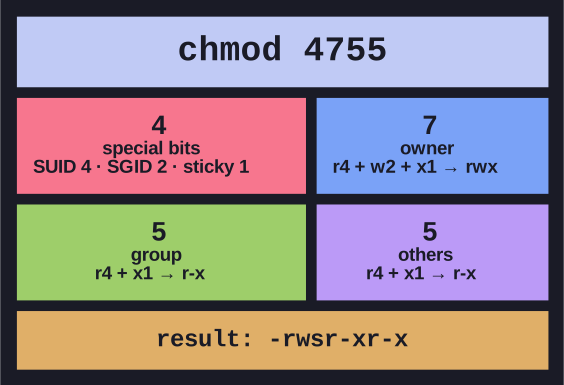
* Four digits: special bits, then one digit per class, each the sum of r4, w2 and x1. *
| Digit | Rights |
|---|---|
| 7 = 4+2+1 | rwx |
| 6 = 4+2 | rw- |
| 5 = 4+1 | r-x |
| 4 | r-- |
| 0 | --- |
chmod 644 filegivesrw-r--r--: the owner reads and writes, everyone else reads.chmod 600 filegivesrw-------: only the owner can do anything. This is the right setting for something like a file of financial data or an SSH private key.chmod 755 dirgivesrwxr-xr-x, the normal mode of a new directory.
The full form has four digits. The optional first one holds the special bits: SUID = 4, SGID = 2, sticky = 1. So chmod 1777 /tmp gives rwxrwxrwt, and chmod 4755 sets SUID on a program.
Worked example: a directory is rwxr-xr-x (755), and others should get write as well. Others become rwx = 7, so the command is chmod 757.
Go deeper:
- Wikipedia: chmod — octal and symbolic modes with many examples.
- man7.org: chmod(1) — the reference, including the special-bit digit.
Note saved — thanks!