Who creates IAM standards, and which well-known standards come from which body?
A mix of standards bodies, consortia, companies and states: for example ITU (X.500), IETF (LDAP, Kerberos, OAuth, SCIM), OASIS (SAML, XACML, SPML, OData), OpenID Foundation (OpenID Connect), W3C and FIDO Alliance (WebAuthn, FIDO2) and vendors such as Microsoft (NTLM, Active Directory).
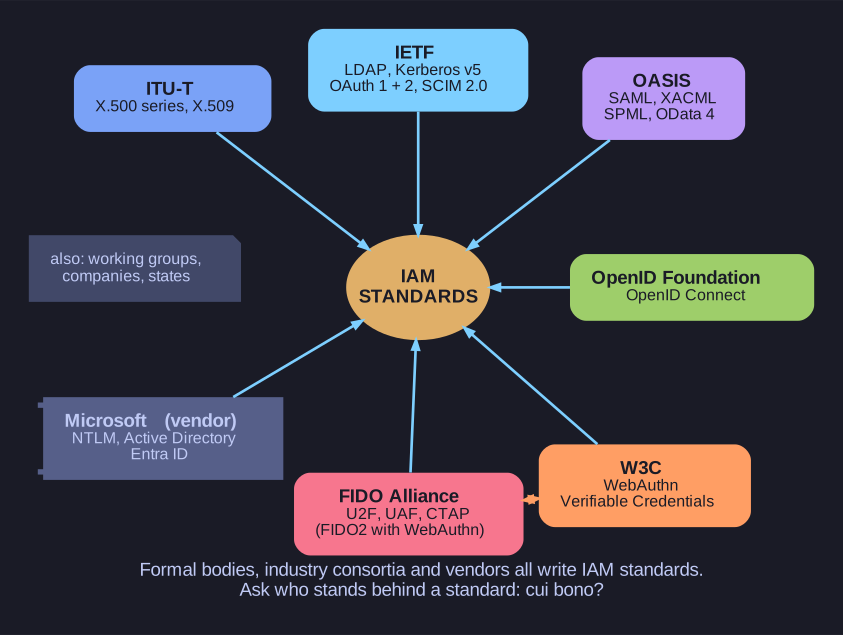
* Who writes which IAM standard: formal bodies, industry consortia and a vendor. *
The players (IAM-Mitspieler) are committees, consortia, working groups, companies, organisations and even states:
| Player | Kind | Typical IAM standards |
|---|---|---|
| ITU-T | UN telecom standards body | X.500 directory series (including X.509 certificates) |
| IETF | Open Internet standards community | LDAP, Kerberos v5, OAuth 1.0 and 2.0, SCIM 2.0 |
| OASIS | Industry standards consortium | SAML, XACML, SPML, OData 4 |
| OpenID Foundation | Non-profit foundation | OpenID Connect |
| W3C | Web standards consortium | WebAuthn, Verifiable Credentials |
| FIDO Alliance | Industry alliance | U2F, UAF, CTAP (with WebAuthn = FIDO2) |
| Microsoft | Vendor | NTLM, Active Directory, Entra ID (OData began here before moving to OASIS) |
On top of the standards sit the tools: commercial software, freeware, open-source products, IAM-as-a-service and cloud services, each implementing some subset of the standards. Knowing who stands behind a standard helps to judge it: an IETF RFC is open and consensus-driven, while a vendor protocol follows that vendor's product strategy.
Go deeper:
 IETF: Introduction — how the body behind LDAP, Kerberos, OAuth and SCIM works.
- OASIS Open (Wikipedia) — the consortium behind SAML, XACML, SPML and OData.
- Standards organization (Wikipedia) — formal bodies versus consortia versus vendor standards.