Which standards do Windows Active Directory, Microsoft Entra ID and university federations each bundle?
Active Directory (on premises) bundles Kerberos, NTLM and LDAP; Microsoft Entra ID (cloud, formerly Azure AD) bundles OpenID Connect/OAuth 2, SAML 2, SCIM and OData-based APIs; universities typically federate with Shibboleth, a SAML implementation.
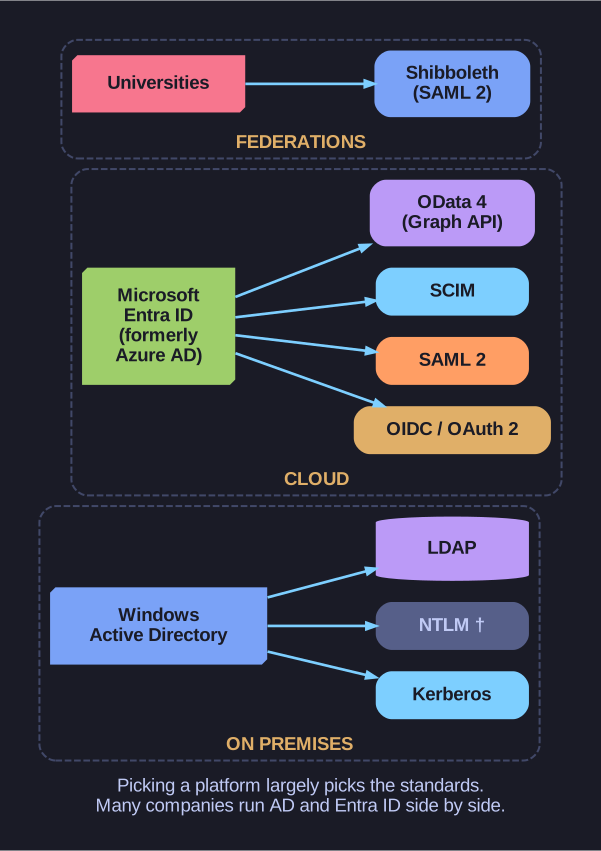
* Products are bundles of standards: the old platform speaks the on-premises protocols, the new one the web protocols. *
In practice you rarely pick standards one by one; you pick a platform, and it brings its standards with it:
- Windows Active Directory (on premises): LDAP for the directory, Kerberos as the main authentication protocol, NTLM as the legacy fallback.
- Microsoft Entra ID (cloud; renamed from Azure Active Directory in 2023): OpenID Connect and OAuth 2.0 for modern apps, SAML 2.0 for enterprise single sign-on, SCIM to provision accounts into SaaS applications, and the Microsoft Graph API, which uses OData query conventions. It deliberately does not use Kerberos and LDAP as its core protocols.
- Universities (Hochschulen): Shibboleth, an open-source SAML implementation, is the classic way to federate logins between institutions.
The consequence for IAM decisions: choosing a platform largely decides which standards your applications must speak, and a company running both AD and Entra ID (very common) has to keep both worlds in sync.
Go deeper:
 Active Directory (Wikipedia) — AD's use of LDAP and Kerberos, and how Entra ID differs.
- Microsoft: New name for Azure Active Directory — the 2023 rename to Microsoft Entra ID.
- Shibboleth (software) (Wikipedia) — the SAML-based federation software used by universities.