Quiz Entry - updated: 2026.10.22
Which parameters define an LDAP search, and what do the three search scopes mean?
A search is defined by a base DN (where to start), a scope (base, one level or whole subtree), a filter (which entries match) and an attribute list (what to return); the scope decides how far below the base the server looks.
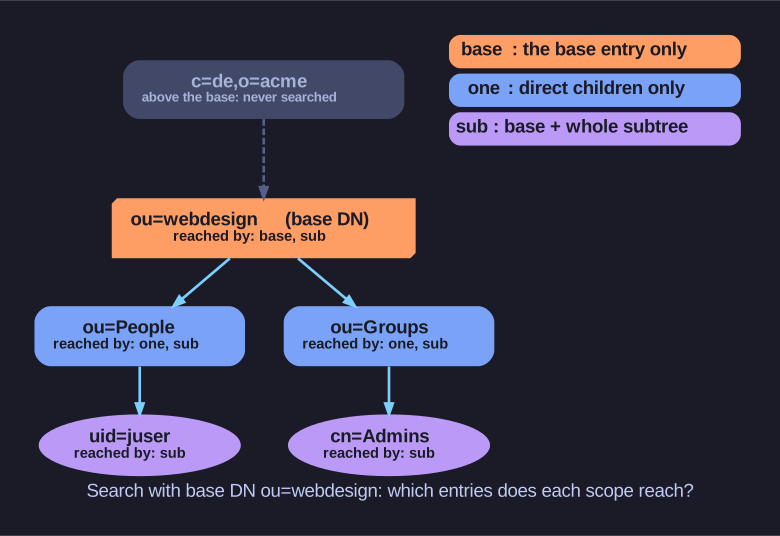
* The same base DN, three scopes: how deep the server looks below the starting point. *
| Scope | ldapsearch -s |
Searches |
|---|---|---|
| base (baseObject) | base |
Only the base entry itself; used to read one known entry |
| one level (singleLevel) | one |
Only the direct children of the base, not the base itself |
| subtree (wholeSubtree) | sub |
The base entry and everything beneath it, at any depth |
Further parameters limit the result: a size limit and a time limit, and whether only attribute names or also values are returned. Choosing a narrow base and scope matters for performance on large directories: searching ou=People,o=acme with scope one is much cheaper than searching o=acme with scope sub.
Go deeper:
 LDAP.com: The LDAP search operation — base DN, scope, filter, attribute list and the limits, one by one.
- RFC 4511, Section 4.5.1: Search Request — the normative list of search parameters.