Quiz Entry - updated: 2026.10.22
Which key protects which item in the Kerberos exchanges?
Client secret key → TGS session key (AS reply); KDC key → TGT; TGS session key → client authenticator to the TGS and the service session key (TGS reply); service secret key → service ticket; service session key → authenticators between client and service.
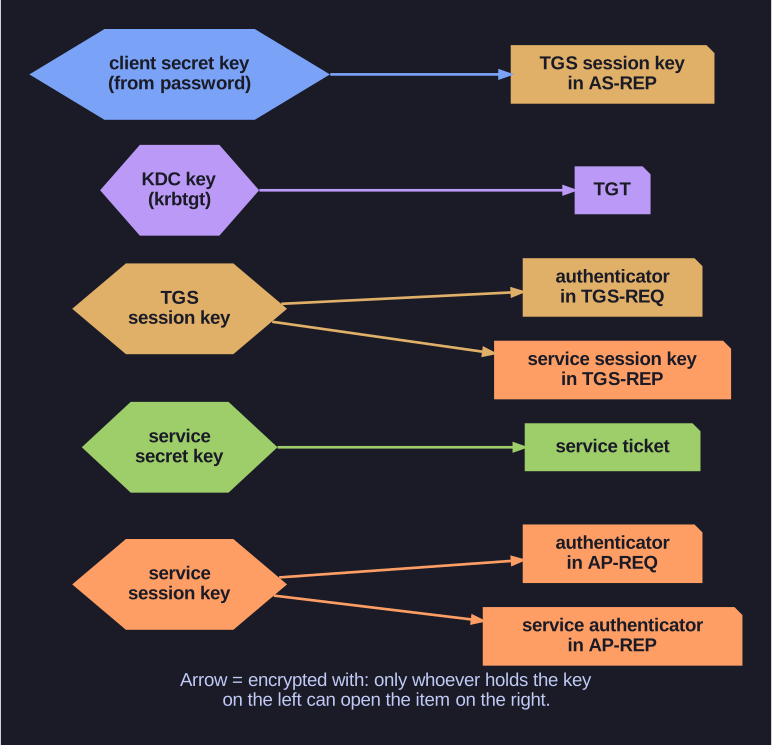
* Each item is locked with a key that only its intended reader has. *
| Item | Encrypted with | Who can open it |
|---|---|---|
| TGS session key (in AS-REP) | Client secret key | Client (and KDC) |
| TGT | KDC key | Only the KDC (AS/TGS) |
| Authenticator in TGS-REQ | TGS session key | TGS (after opening the TGT) |
| Service session key (in TGS-REP) | TGS session key | Client |
| Service ticket | Service secret key | The service (and KDC) |
| Client authenticator in AP-REQ | Service session key | Service (after opening the ticket) |
| Service authenticator in AP-REP | Service session key | Client |
The pattern behind the table: each session key is delivered twice, once to the client (under a key the client already has) and once inside a ticket (under a key only the next server has). That is how two parties who never met end up sharing a fresh secret.
Go deeper:
 Roguelynn: Explain like I'm 5, Kerberos — follows each message and spells out which key opens what.