Quiz Entry - updated: 2026.10.20
What are typical places where perimeter security is used?
- Separating the internet (outside) from the internal company network
- Separating clients and user devices from the servers in the backbone
- Separating IT from OT
- Segmenting the network into security zones (e.g. mission-critical servers, regular servers, internal clients, guest LAN)
- Building a DMZ
- Building private cloud zones
- Cutting off high-security areas
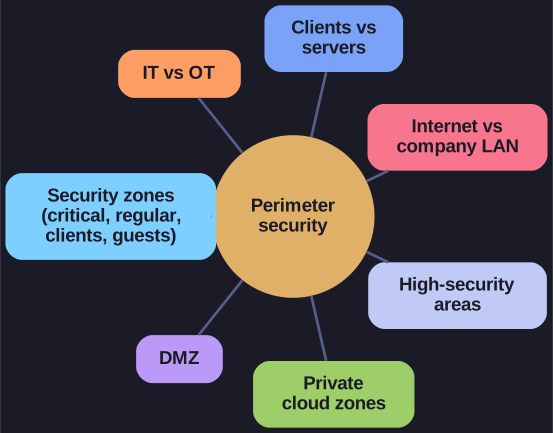
* The same pattern, a regulated border between groups, applied at many places in one estate. *
The common thread is that each case has a group of systems that should talk freely among themselves and only in a controlled way with everything else. A DMZ ("demilitarised zone") is a zone between the internal network and the internet for systems that must be reachable from outside, such as a public web server, so that those systems sit behind their own perimeter and not inside the company network.
Go deeper:
 DMZ (computing) — Wikipedia — single- and dual-firewall DMZ designs.
- Network segmentation — Wikipedia — why splitting a network into zones limits damage.
- NIST SP 800-82 Rev. 3 — Guide to OT Security — IT/OT separation and segmentation for industrial networks.