Quiz Entry - updated: 2026.10.22
What are the three parts of the Kerberos protocol, and which parties talk in each?
- Part 1 (steps 1-2), client and AS: negotiate the TGS session key and issue the encrypted TGT.
- Part 2 (steps 3-4), client and TGS: issue a service ticket.
- Part 3 (steps 5-6), client and service: mutual authentication and a shared session key.
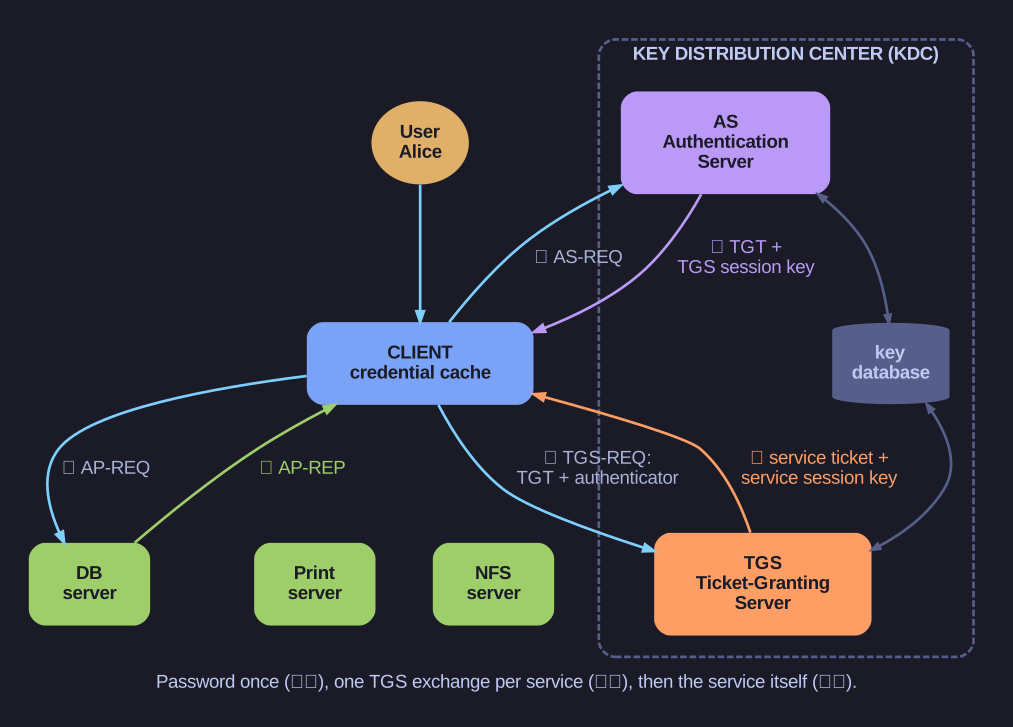
* Six messages in three exchanges: AS for the TGT, TGS for the service ticket, then the service itself. *
| Part | Messages | Purpose |
|---|---|---|
| 1: AS exchange | ① AS-REQ, ② AS-REP | Log in once: get the TGT and the TGS session key |
| 2: TGS exchange | ③ TGS-REQ, ④ TGS-REP | Swap the TGT for a ticket to one service |
| 3: Client/server exchange | ⑤ AP-REQ, ⑥ AP-REP | Present the ticket; client and service authenticate each other |
The structure explains the SSO effect: part 1 happens once per login (usually per working day), part 2 once per service, and part 3 whenever a connection to a service is opened. The password is needed only in part 1, and only on the client.
Go deeper:
 RFC 4120, Section 3: Message exchanges — the AS, client/server and TGS exchanges in full detail.
 Computerphile: Taming Kerberos — the three exchanges drawn and explained.
- Kerberos protocol description (Wikipedia) — message-by-message description with the same structure.