Quiz Entry - updated: 2026.10.22
How does passwordless authentication differ from multi-factor authentication?
They answer different questions: passwordless says no password is used, MFA says at least two distinct factors are used. A method can be passwordless but single-factor, and MFA may well include a password as one of its factors.
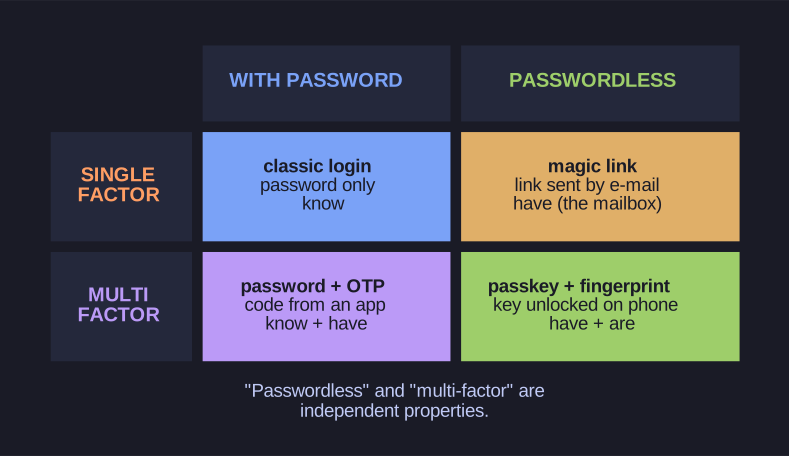
* Two independent axes: whether a password is used, and how many distinct factors are combined. *
The two properties are independent, so all four combinations exist:
- Password, single-factor: the classic login.
- Password, multi-factor: password plus an authenticator-app code.
- Passwordless, single-factor: a magic link. It only proves access to the mailbox, a single possession factor, and is only as strong as the mail account.
- Passwordless, multi-factor: a passkey on a phone unlocked by fingerprint (have + are), or a smartcard with a PIN (have + know, where the PIN is checked locally and is not a server password).
So "passwordless" is not automatically "stronger". The security comes from what replaces the password: a phishing-resistant key with local activation is excellent; a link in an e-mail mostly moves the risk to the mail account.
Go deeper:
 Passwordless authentication: Benefits and drawbacks (Wikipedia) — where passwordless helps and what new risks it introduces.