Company B's policy demands a WAF, but no cloud WAF can protect its Blazor Server app. How does it resolve the dilemma?
It approves a documented exception to the WAF policy, under conditions: the web application gets an initial, thorough penetration test with bug fixing, and the pen test and bug fixing are repeated regularly whenever the application changes. Since the cloud provider's offering keeps changing, the company hopes for a provider solution soon.
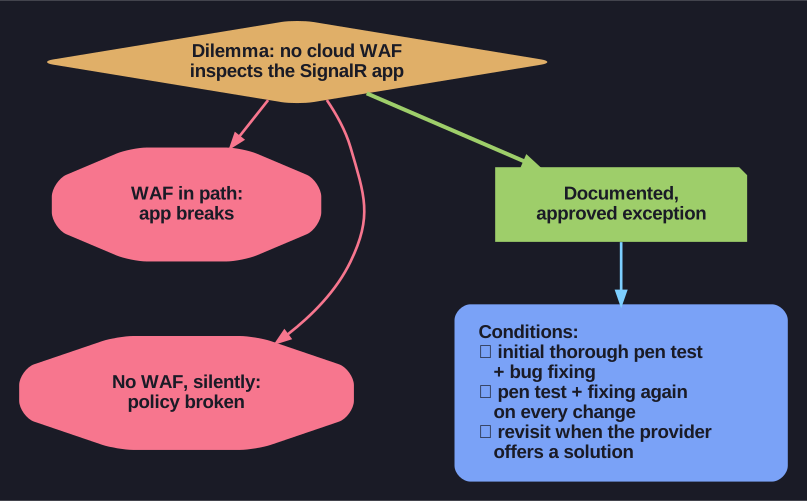
* Neither branch of the dilemma is acceptable, so the policy gets a controlled, documented exception. *
The dilemma: either the web application doesn't work (WAF in the path breaks the sockets), or it works without the extra protection and the company policy is broken. Silently breaking the policy would be the worst outcome, since nobody would know the risk exists. A documented exception makes the gap visible, puts a decision-maker's name on it, and ties it to compensating controls. Penetration testing (an authorised, simulated attack to find exploitable weaknesses) covers what the WAF would have caught by finding and fixing the flaws in the application itself, and repeating it after changes keeps that true over time. The exception should also be revisited when the provider's offering improves.
Tip: an exception is a control too, but only if it is written down, approved, conditioned and reviewed.
Go deeper:
 Penetration test — Wikipedia — what a pen test is and how it is run.
- Microsoft Learn — WebSocket on Azure Front Door — how the provider's offering has moved since, and what its WAF still doesn't inspect.