Building a segmented n-tier DMZ on premises quickly runs out of firewalls. What is the way out?
Hardware firewalls are usually expensive and need a lot of care, so on premises too the step to virtualisation makes sense: firewalls can be installed as firewall software modules or, in the simplest case, as IP filters directly on each resource.
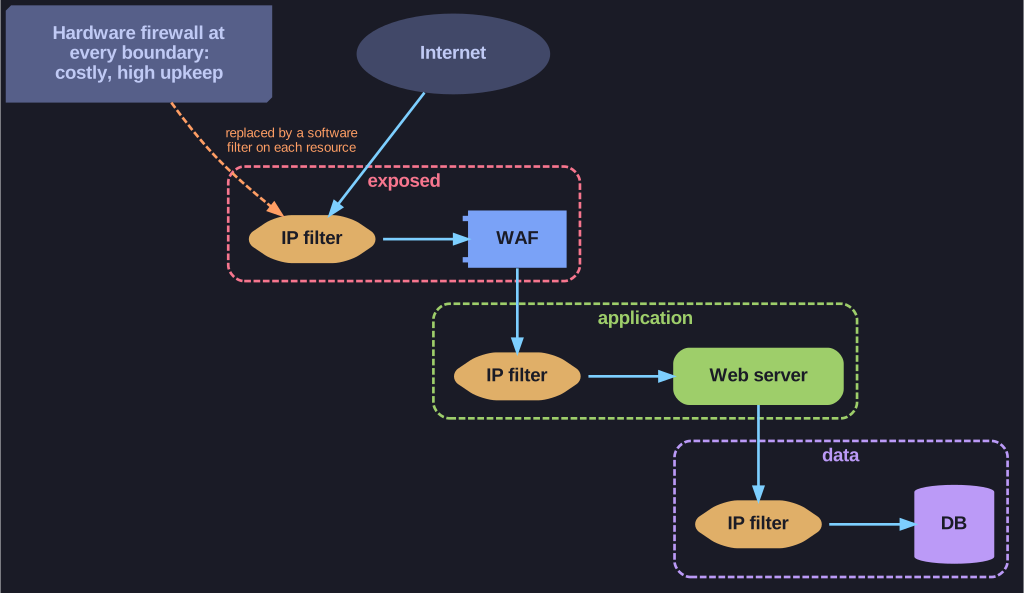
* Instead of a hardware box between every pair of zones, each resource filters its own traffic. *
Every extra zone boundary in the n-tier picture would otherwise mean another physical firewall to buy, rack, patch and monitor. Moving the filter onto the resource itself (a host firewall such as iptables/nftables on Linux, the Windows firewall, or a virtual firewall in the hypervisor) makes segmentation cheap enough to do at every tier: the WAF, the web server and the database each enforce "only my neighbour tier may talk to me". This is the same idea that, taken further, becomes micro-segmentation.
Go deeper:
 Microsegmentation (network security) — Wikipedia — host-firewall, host-agent and hypervisor segmentation compared.
- iptables — Wikipedia — the classic Linux host-based packet filter.