Beyond the missing input validation, which technical security problems does publisher Z's years-old LAMP platform likely have?
An outdated stack (Linux, Apache, MySQL and PHP all affected) with missing security patches, weak passwords and passwords stored in configuration files for technical accounts, open ports of unknown status, old and weak cryptography, no security software such as anti-virus or intrusion detection/prevention, a backend connection that enables lateral movement, a data-leak risk for customer and payment data, and a system that doesn't scale against modern attacks such as DDoS and bots.
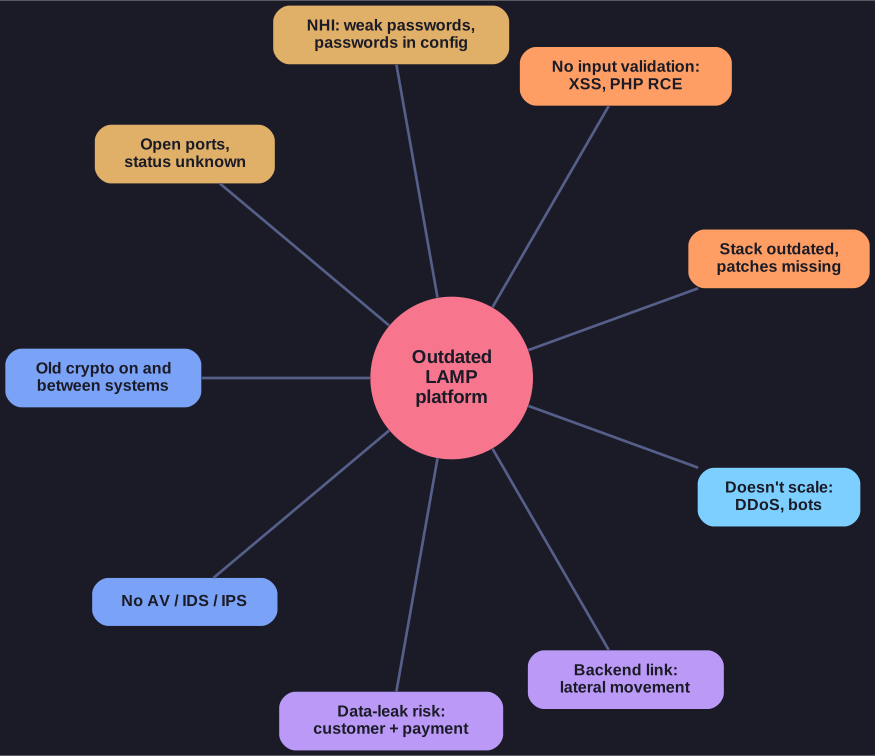
* Almost every layer of an unmaintained stack contributes its own risk. *
| Area | Likely problem | Why it matters |
|---|---|---|
| Software state | Outdated LAMP stack, patches missing for OS, PHP, Apache, DB | Known, published vulnerabilities stay open: high risk |
| Code | Input validation missing | XSS, PHP remote code execution |
| Technical identities | Weak passwords, passwords in config files | Non-human identities (NHI: service accounts, DB users) are easy to steal or guess |
| Network | Open ports, status unknown | Unneeded services as extra entry points |
| Cryptography | Old systems, old algorithms on and between systems | Data readable or forgeable in transit and at rest |
| Protection | No anti-virus, IDS/IPS or similar | Attacks go unnoticed |
| Data and backends | Customer data, payment means; backend connection | Data leaks; a compromised platform as a springboard into internal systems |
| Capacity | Doesn't scale | Modern attacks (DDoS, bots) overwhelm an old system |
The common thread is age without maintenance: none of these is exotic, but together they make the platform the easiest target the publisher has on the internet.
Go deeper:
 OWASP Top 10 — the standard list of the most critical web-application risks, most of which apply here.
- OWASP Non-Human Identities Top 10 — risks of service accounts and machine credentials, including secrets in config files.
- OWASP Cheat Sheet — Secrets Management — keeping passwords out of configuration files.